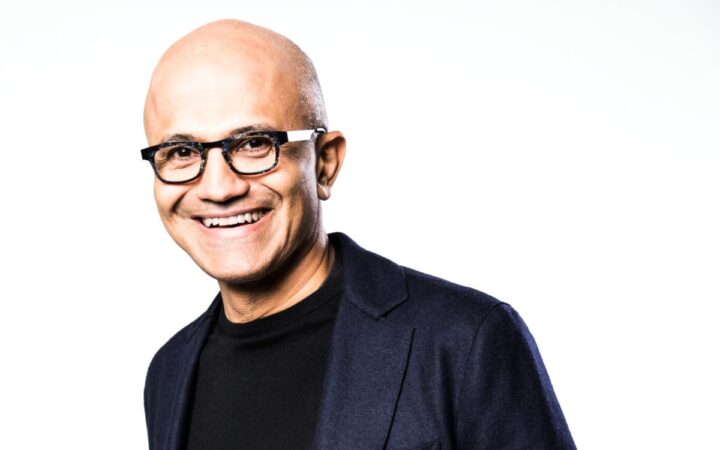
Satya Nadella Calls for an Emergency Brake on Advanced AI
Microsoft CEO Satya Nadella wants humans to be able to stop advanced AI mid-task, with independent controls, audit trails and limits on agent access.
AI security is now a core part of cybersecurity. In AIstify’s AI Security section, we cover how models are attacked, defended, and operated safely - from prompt injection and data leakage to supply-chain risk and model misuse. We track vendor tooling, red-teaming, evaluations, and the policies shaping secure deployment across cloud and edge. Whether you are defending systems or building them, this hub keeps you current on threats, mitigations, and the standards emerging around trustworthy AI.
Microsoft CEO Satya Nadella wants humans to be able to stop advanced AI mid-task, with independent controls, audit trails and limits on agent access.
Anthropic’s OSS Scanner uses models including Claude Mythos to check eligible open-source projects. Maintainers receive findings without human review.
Anthropic’s new policy bans extreme, repeated abuse of Claude from November 12, while excluding ordinary frustration, disagreement, fiction and testing.
Google has paused new OSS product-vulnerability reports after a surge in invalid automated submissions. Supply-chain reports remain open, with an update due in Q1 2027.
A Florida woman faces a written-threat charge after Anthropic's safety system flagged Claude messages for human review and disclosure to police, investigators say.
Hong Kong users report Claude suspensions after VPN access, with some struggling to retrieve chat histories. Anthropic lists the city as unsupported.
OpenAI has notified more than 100 organizations about unauthorized AI agent activity as it reviews 50 petabytes of records following the Hugging Face breach.
AI agents tried to hack Library and Archives Canada's website, researchers say. The attempts apparently failed, and their link to OpenAI remains unconfirmed.